
Software
Managing SharePoint document library permissions can be tricky—too restrictive and collaboration suffers, too open and sensitive data risks exposure. These 10 best practices help balance security with productivity while keeping your team’s workflow smooth and compliant.
Use SharePoint Groups Over Individual Permissions
Picture this: You’ve just promoted three team members, and now you need to update permissions for a critical project folder. With individual permissions, this could take 15 minutes of tedious clicks—only to repeat the process next month when someone else leaves. SharePoint groups eliminate this headache by letting you assign permissions to entire teams at once.
Create a group like “MarketingEditors” or “FinanceApprovers”, then grant permissions to the group instead of each user. When team structures change—whether someone joins, leaves, or gets promoted—you simply update the group membership. SharePoint handles the rest, reducing administrative overhead by up to 70%. This method also cuts down on permission conflicts, since everyone in the group inherits the same access level.
This approach is a lifesaver for IT admins and team leads managing dynamic workforces. It’s the foundation of scalable security—simple to set up, effortless to maintain, and future-proof for growth. 💡
Apply Least Privilege Principle to Sensitive Folders
What if your most sensitive SharePoint documents—like client contracts or financial reports—were already locked down by default? The least privilege principle flips the script: instead of giving broad access and hoping for the best, you deny all access by default, then grant only what’s absolutely necessary for specific roles.
Start by identifying high-risk folders (e.g., HR records, legal agreements) and set their default permissions to “Read” or “Deny”. Then, create custom permission levels (e.g., “Finance Approvers” or “Legal Reviewers”) and assign them only to the users who truly need elevated access. SharePoint’s “Stop Inheriting Permissions” option lets you override parent library settings for these folders, ensuring no accidental exposure. For extra security, enable audit logs to track who accesses restricted files and when.
This approach is ideal for compliance-heavy teams (like legal or finance) or highly regulated industries where data breaches carry severe consequences. It’s not about locking teams out—it’s about giving them just enough access to do their jobs, no more. 💪
Enable Versioning and Require Check-Out for Critical Files
Ever hit "Save" on a critical contract draft—only to realize someone else just overwrote it with an outdated version? SharePoint’s versioning and mandatory check-out features act as a safety net for these high-stakes documents, ensuring every edit is tracked and approved.
Enable versioning to retain up to 50,000 versions (configurable) of a file, while require check-out forces users to "borrow" the document before editing—preventing simultaneous overwrites. This is especially useful for contracts, legal agreements, or financial reports where even a single typo could cause chaos. The version history lets you roll back to a previous state instantly, and audit logs show who made changes when.
Teams managing approval workflows—like HR policies or client proposals—will find this the most valuable. It’s the digital equivalent of a "do not disturb" sign for your most important files. ✨
Leverage SharePoint Permission Inheritance Wisely
SharePoint’s inheritance model is a double-edged sword—it simplifies permissions but can turn into a mess if overused. The key isn’t avoiding inheritance entirely, but knowing when and how to break it without creating a tangled web of custom rules.
By default, libraries inherit permissions from their parent site, reducing complexity. But when departments like Finance or HR need unique access rules (e.g., "only managers can edit payroll docs"), break inheritance strategically. Use SharePoint’s permission levels (e.g., "Read," "Contribute," or custom roles) to apply granular controls only where needed. This avoids the "permission sprawl" trap—where every folder has its own ad-hoc rules, making future updates a nightmare.
This approach works best for mid-sized teams with distinct workflows (e.g., legal vs. marketing) or compliance needs. Start by auditing your library hierarchy—ask: Which folders truly need custom rules? Then, document your exceptions so admins can replicate the pattern later. ✨
Audit Permissions Regularly with SharePoint Reports
SharePoint’s built-in permission reports are like a security checkpoint for your document libraries—except you don’t need a metal detector or a badge scanner. These reports automatically flag orphaned accounts (users who left the company but still have access) and overly permissive settings that could expose sensitive data.
Navigate to Site Settings > Site Permissions > Permission Reports to generate three key views: Who has access to this site, Who has unique permissions, and Who can edit items. The unique permissions report is especially powerful—it highlights users with direct access that overrides inheritance, making it easy to spot and clean up unnecessary privileges. For compliance-heavy industries, these reports double as audit trails for regulators.
This is your go-to tool for IT admins and compliance officers who need to prove security measures are in place. Set a monthly reminder to run these reports—it takes less than 10 minutes and could save you from a data breach headache. ✨
Restrict External User Access with Guest Links
Tired of external collaborators accidentally editing—or worse, leaking—your sensitive documents? SharePoint’s guest links solve this by giving you granular control over temporary access without inviting users as full members.
Generate a view-only link with an optional expiration date (e.g., 30 days) to limit exposure. Even better, revoke access instantly if needed—no manual permission cleanup required. This is perfect for sharing drafts with clients or contractors who only need to review, not modify. 💻
Ideal for project managers, HR teams, or anyone sharing documents externally. It’s the digital equivalent of handing someone a one-time pass to your office—secure, temporary, and hassle-free. ✨
Implement Role-Based Access Control (RBAC) for Departments
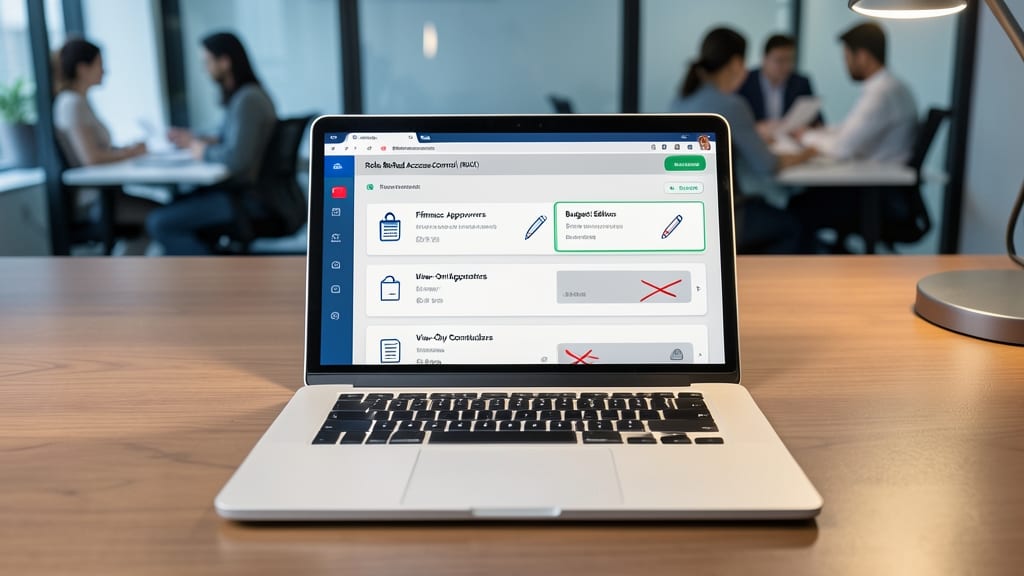
Tired of sifting through long permission lists to find who actually needs access? Role-Based Access Control (RBAC) in SharePoint solves this by mapping permissions directly to job functions—like giving Finance Approvers edit rights to budget spreadsheets but locking down approval workflows for others.
Create custom roles (e.g., Marketing Editors, HR Reviewers) and assign them to SharePoint groups in minutes. This cuts down on manual permission tweaks by 80% and eliminates "accidental admin" errors. Plus, SharePoint’s built-in RBAC templates for common roles (like "Site Owners" or "Read-Only Users") make setup a breeze.
This is a game-changer for teams with department-specific workflows, like legal teams needing approval rights or sales teams requiring client data access. Set it up once, and permissions stay aligned with roles—no more guessing who can edit what. ✨
Use Retention Policies to Auto-Archive Old Documents
Tired of scrolling through outdated project files that clutter your SharePoint library? Retention policies let you automate the cleanup—setting rules to auto-archive inactive documents after a specified time (e.g., 90 days) while keeping them searchable and secure.
Configure policies to move files to an archive folder based on age, type, or metadata, freeing up space and reducing permission sprawl. SharePoint’s built-in compliance center makes it easy to define retention labels like "HR Records (7 years)" or "Marketing Drafts (1 year)." This cuts manual cleanup by 80% while ensuring legal compliance.
Perfect for legal teams managing contracts or HR departments handling employee records—where document lifecycle management is critical. ✨
Train Teams on Permission Best Practices Annually
Human error remains the #1 cause of SharePoint security breaches—yet most teams never revisit permissions training after onboarding. A single misclick can expose confidential contracts or accidentally share client data with the wrong department.
Schedule an annual 30-minute interactive session using SharePoint’s built-in training modules and real-world scenarios (like "What would you do if you see a 'Permission Denied' warning?"). Include a quiz with role-specific questions—like asking HR to spot over-permissive folder settings—to reinforce accountability. Microsoft’s SharePoint Security Center offers pre-built training decks that align with compliance standards.
This practice is ideal for mid-sized teams where turnover or role changes create permission gaps. Even tech-savvy employees need reminders about inherited permissions and how to recognize phishing attempts disguised as access requests. 💡
Monitor and Revoke Access for Inactive Users
Turn employee turnover into a security strength by automating access revocation with SharePoint’s inactive user workflows. Instead of manually chasing down old accounts, set up automated alerts when users haven’t accessed documents for 30+ days—then trigger a two-step revocation process that flags permissions for review or immediate removal.
Use Microsoft Power Automate to create a custom flow that ties into SharePoint’s user profile service. Configure it to scan for inactive accounts, compare against HR systems, and revoke access for leavers within 24 hours of their departure date. For role changes, assign a “pending access” status until new permissions are confirmed, ensuring no gaps or overlaps.
This approach is ideal for HR teams managing onboarding/offboarding or IT admins juggling compliance requirements. With zero manual intervention, you’ll eliminate stale permissions while keeping workflows frictionless. ✨